cirse.org
Last scanned August 24, 2026
A cookie scan of cirse.org performed on August 24, 2026 found 11 cookies and 5 third-party tracking requests. The assessment covered 10 pages across 10 unique page templates. The site employs CookieYes as its consent management platform. Neither IAB TCF v2.3 nor Google Consent Mode v2 was observed on our check. 5 third-party requests were detected from 3 vendors.

Consent behaviour grade
28 / 100
This site set multiple tracking cookies before the visitor consented. Under ePrivacy Article 5(3), these require prior consent.
Automated point-in-time check of the scanned pages; not legal advice. How our check works.
Consent enforcement level
-
1
Nothing non-essential runs before consent is given. This is the strict reading of ePrivacy Article 5(3) and the strongest position.
-
2
Google tags load with storage defaulted to denied and send only cookieless pings before consent. Permitted in Google's model, but not the strict reading of Article 5(3).
-
3
Google Consent Mode v2 restrains Google tags, but other trackers or cookies were observed before consent.
-
4
Runs before consent This site
A consent banner is present but does not restrain tracking. Trackers and cookies run before the visitor consents.
Consent banner as encountered
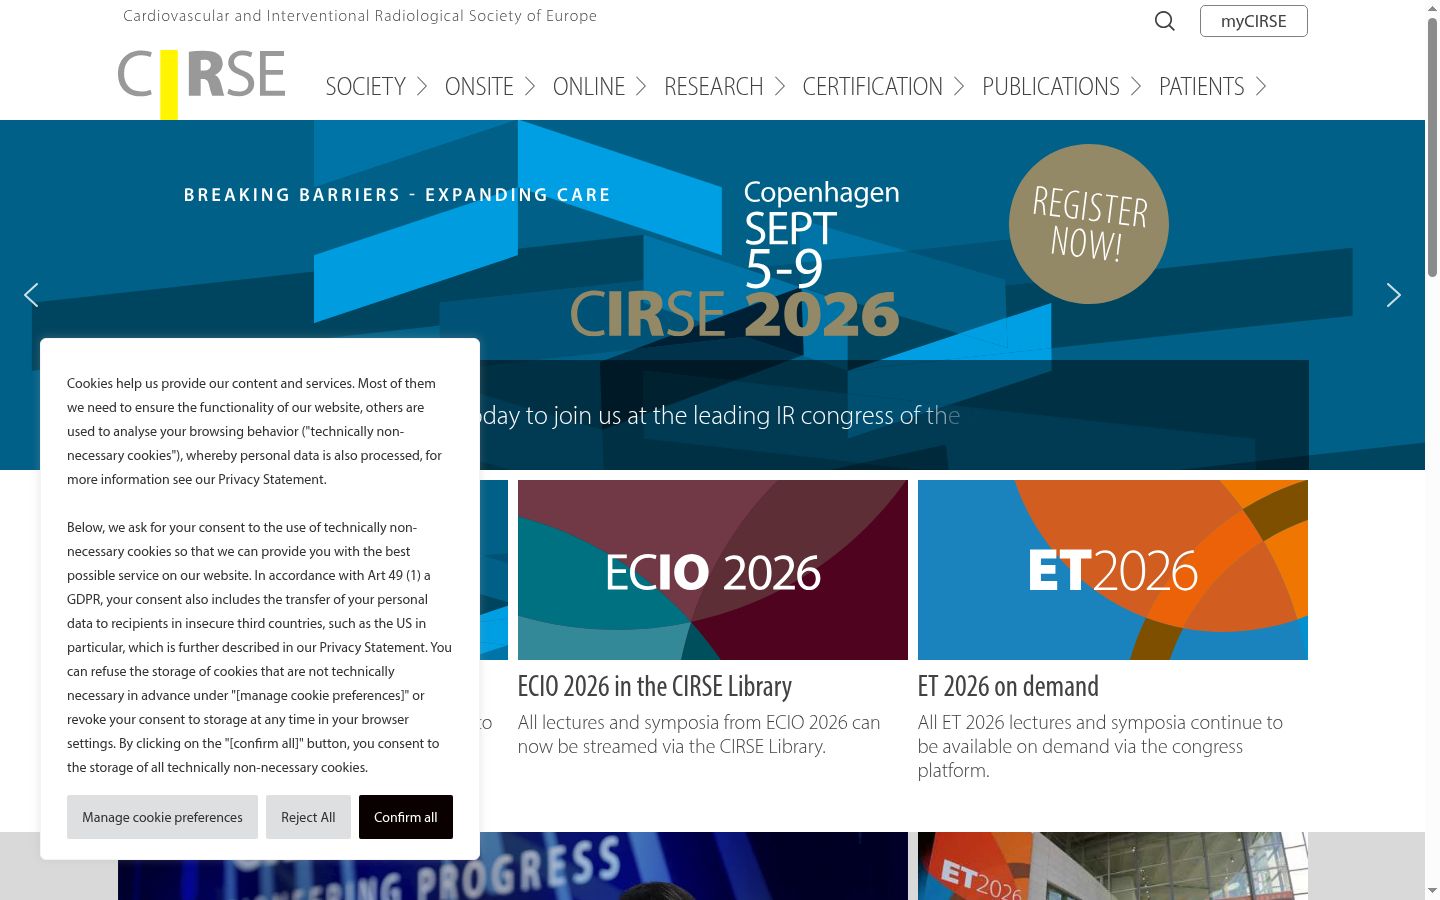
The first layer offers a Reject option alongside Accept.
Load timeline before consent
Milliseconds from navigation start until each request fired or each cookie was set.
Observed before consent
Cookies set before consent (10)
-
_pk_id.1.21eaanalytics · Matomo -
_pk_ses.1.21eaanalytics · Matomo -
sbjs_currentanalytics · WooCommerce -
sbjs_current_addanalytics · WooCommerce -
sbjs_firstanalytics · WooCommerce -
sbjs_first_addanalytics · WooCommerce -
sbjs_migrationsanalytics · WooCommerce -
sbjs_sessionanalytics · WooCommerce -
sbjs_udataanalytics · WooCommerce -
__cflbnecessary · Cloudflare
Tracking requests before consent (4)
- Google LLC www.googletagmanager.com at 1250 ms
- Adobe Fonts use.typekit.net at 1229 ms
- LinkedIn Corporation snap.licdn.com set by analytics.cirse.org/container_wZiXYx7T.js · at 1364 ms
- LinkedIn Corporation px.ads.linkedin.com set a cookie set by snap.licdn.com/insight.old.min.js · at 1399 ms
How we tested
Browser: Chrome/150.0.7871.124 · Scan origin: EU · Viewport: 1440×900 · Checked: 24 Aug 2026 17:52 - 24 Aug 2026 17:53
Cookies
11
Third-party
0
Trackers
5
Vendors
3
Consent banner
CookieYes
Scans
1
What this setup is missing
- Google tags were observed, but Google Consent Mode v2 was not detected.
Compliance by audience
European Union
✗ Not metGDPR + ePrivacy · Prior consent (opt-in)
United Kingdom
✗ Not metUK GDPR + PECR · Consent-based
United States
✓ Meets this modelCCPA/CPRA + state laws · Notice & opt-out
Canada
! Needs attentionPIPEDA + Québec Law 25 · Consent-based
Brazil
! Needs attentionLGPD · Consent-based
Scanned from the EU; sites may serve different banners or tracking to other regions. Verdicts reflect observed behaviour measured against each audience's rules.
Connection security
HTTPS supported
✓Redirects HTTP to HTTPS
✓HSTS
✓Content Security Policy
✗
Third-Party Trackers
5 requests detected from 3 vendors: Google LLC, Adobe Fonts, LinkedIn Corporation
Third-Party Trackers
5 requests detected from 3 vendors: Google LLC, Adobe Fonts, LinkedIn Corporation
Analytics
1
Marketing
2
Necessary
1
Functional
1
Other
0
| Vendor | Category | Type | Domain |
|---|---|---|---|
| Google LLC before consent Google Tag Manager | Analytics | script | www.googletagmanager.com |
| Adobe Fonts before consent Adobe Fonts (Typekit): web font delivery | Functional | script | use.typekit.net |
| LinkedIn Corporation before consent LinkedIn Insight Tag | Marketing | script | snap.licdn.com |
| LinkedIn Corporation before consent LinkedIn Ads tracking | Marketing | pixel | px.ads.linkedin.com |
| Google LLC Google Fonts stylesheet | Necessary | script | fonts.googleapis.com |
Scan history
One completed scan: cookies and trackers from the scan on August 24, 2026.
Recent scans
| August 24, 2026 | 11 5 |
More Cookie Compliance Reviews

Security Verification
hokun-trust.org

HokiTem Buku Mimpi 2D - HokiTem
hokitem.org

Log In ‹ hokitan — WordPress
hokitan.org

Index of /
hokispbu22.org

Radar Sports Betting — Analyses des opérateu...
hokispin99.org

Hokiplay88 | Platform Modern Aman Stabil Terukur
hokiplay88.org

Hokiplay | Gaming Modern Berkualitas Semua Kebu...
hokiplay.org

Messages
hokibet855.org
Is cirse.org your website?
Claim it to monitor your cookies and trackers, set up a consent banner with automatic script blocking, and keep your cookie policy up to date.