hyper.one
Last scanned October 1, 2026
A cookie scan of hyper.one completed on October 1, 2026 found 4 cookies and 8 third-party tracking requests. The assessment covered 9 pages across 9 unique page templates. The site uses OneTrust as its consent management platform. Neither IAB TCF v2.3 nor Google Consent Mode v2 was observed on our check. 8 third-party requests were detected from 4 vendors.

Consent behaviour grade
60 / 100
This site issued tracking requests before consent. Some of what we observed needs attention.
Automated point-in-time check of the scanned pages; not legal advice. How our check works.
Consent enforcement level
-
1
Nothing non-essential runs before consent is given. This is the strict reading of ePrivacy Article 5(3) and the strongest position.
-
2
Google tags load with storage defaulted to denied and send only cookieless pings before consent. Permitted in Google's model, but not the strict reading of Article 5(3).
-
3
Google Consent Mode v2 restrains Google tags, but other trackers or cookies were observed before consent.
-
4
Runs before consent This site
A consent banner is present but does not restrain tracking. Trackers and cookies run before the visitor consents.
Consent banner as encountered
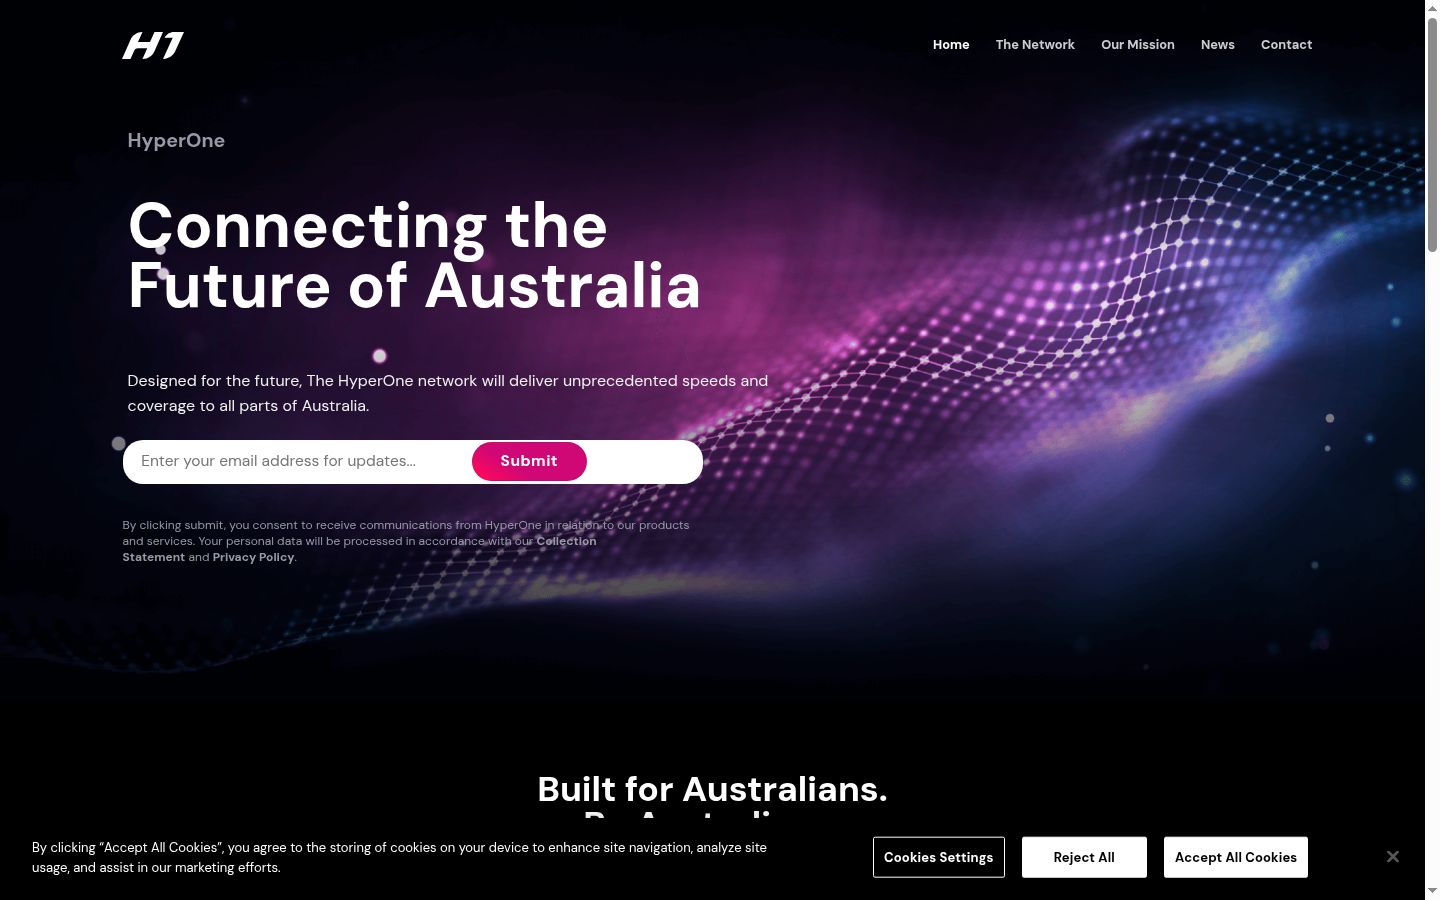
The first layer offers a Reject option alongside Accept.
Load timeline before consent
Milliseconds from navigation start until each request fired or each cookie was set.
Observed before consent
Cookies set before consent (3)
-
_gaanalytics · Google Analytics -
_ga_CZ3PNHEFG1analytics · Google Analytics -
_ga_JTDPKKDLYKanalytics · Google Analytics
Tracking requests before consent (4)
- Google LLC www.googletagmanager.com at 1214 ms
- Sentry (Functional Software) browser.sentry-cdn.com set by fast.wistia.com/E-v1.js · at 2044 ms
- Google LLC www.google.com at 2036 ms
- Google LLC region1.google-analytics.com set by www.googletagmanager.com/js · at 2581 ms
How we tested
Browser: Chrome/150.0.7871.124 · Scan origin: EU · Viewport: 1440×900 · Checked: 1 Oct 2026 09:59
Cookies
4
Third-party
0
Trackers
8
Vendors
4
Consent banner
OneTrust
Scans
1
What this setup is missing
- Google tags were observed, but Google Consent Mode v2 was not detected.
Compliance by audience
European Union
✗ Not metGDPR + ePrivacy · Prior consent (opt-in)
United Kingdom
✗ Not metUK GDPR + PECR · Consent-based
United States
✓ Meets this modelCCPA/CPRA + state laws · Notice & opt-out
Canada
! Needs attentionPIPEDA + Québec Law 25 · Consent-based
Brazil
! Needs attentionLGPD · Consent-based
Scanned from the EU; sites may serve different banners or tracking to other regions. Verdicts reflect observed behaviour measured against each audience's rules.
Connection security
HTTPS supported
✓Redirects HTTP to HTTPS
✓HSTS
✓Content Security Policy
✓
Third-Party Trackers
8 requests detected from 4 vendors: Google LLC, Sentry (Functional Software), Wistia, OneTrust
Third-Party Trackers
8 requests detected from 4 vendors: Google LLC, Sentry (Functional Software), Wistia, OneTrust
Analytics
2
Marketing
0
Necessary
3
Functional
1
Other
2
| Vendor | Category | Type | Domain |
|---|---|---|---|
| Google LLC before consent Google Tag Manager | Analytics | script | www.googletagmanager.com |
| Sentry (Functional Software) before consent Sentry browser SDK | Analytics | script | browser.sentry-cdn.com |
| Google LLC before consent Google reCAPTCHA bot protection | Functional | script | www.google.com |
| Google LLC Google tracker domain (source: Disconnect.me, category: Content) | Necessary | script | www.gstatic.com |
| Google LLC Google Fonts files | Necessary | script | fonts.gstatic.com |
| Wistia Wistia tracker domain (source: Disconnect.me, category: Content) | Necessary | script | fast.wistia.com |
| Google LLC before consent Google tracker domain (source: Disconnect.me, category: FingerprintingGeneral) | Unknown | script | region1.google-analytics.com |
| OneTrust OneTrust tracker domain (source: Disconnect.me, category: ConsentManagers) | Unknown | script | geolocation.onetrust.com |
Scan history
One completed scan: cookies and trackers from the scan on October 1, 2026.
Recent scans
| October 1, 2026 | 4 8 |
More Cookie Compliance Reviews

Homepage - HSC-Schule
hsc-schule.one

HRV
hrv.one

Hopscotch GEO: Managing Reputation in the Age o...
hopscotch.one

Hookah One - Технологии в калья...
hookah.one

One moment, please...
hoesch.one

Transform Complex Sales with AI Solutions | Hig...
hightouch.one

Für Unternehmen
hidden.one

Hackea Tu Cuerpo
hackeatucuerpo.one
Is hyper.one your website?
Claim it to monitor your cookies and trackers, set up a consent banner with automatic script blocking, and keep your cookie policy up to date.