insafedental.eu
Last scanned October 5, 2026
A cookie scan of insafedental.eu conducted on October 5, 2026 found 2 cookies and 5 third-party tracking requests. The assessment covered 4 pages across 4 unique page templates. The site relies on Usercentrics as its consent management platform. Neither IAB TCF v2.3 nor Google Consent Mode v2 was observed on our check. 5 third-party requests were detected from 4 vendors.

Consent behaviour grade
70 / 100
This site issued tracking requests before consent. Some of what we observed needs attention.
Automated point-in-time check of the scanned pages; not legal advice. How our check works.
Consent enforcement level
-
1
Nothing non-essential runs before consent is given. This is the strict reading of ePrivacy Article 5(3) and the strongest position.
-
2
Google tags load with storage defaulted to denied and send only cookieless pings before consent. Permitted in Google's model, but not the strict reading of Article 5(3).
-
3
Google Consent Mode v2 restrains Google tags, but other trackers or cookies were observed before consent.
-
4
Runs before consent This site
A consent banner is present but does not restrain tracking. Trackers and cookies run before the visitor consents.
Consent banner as encountered
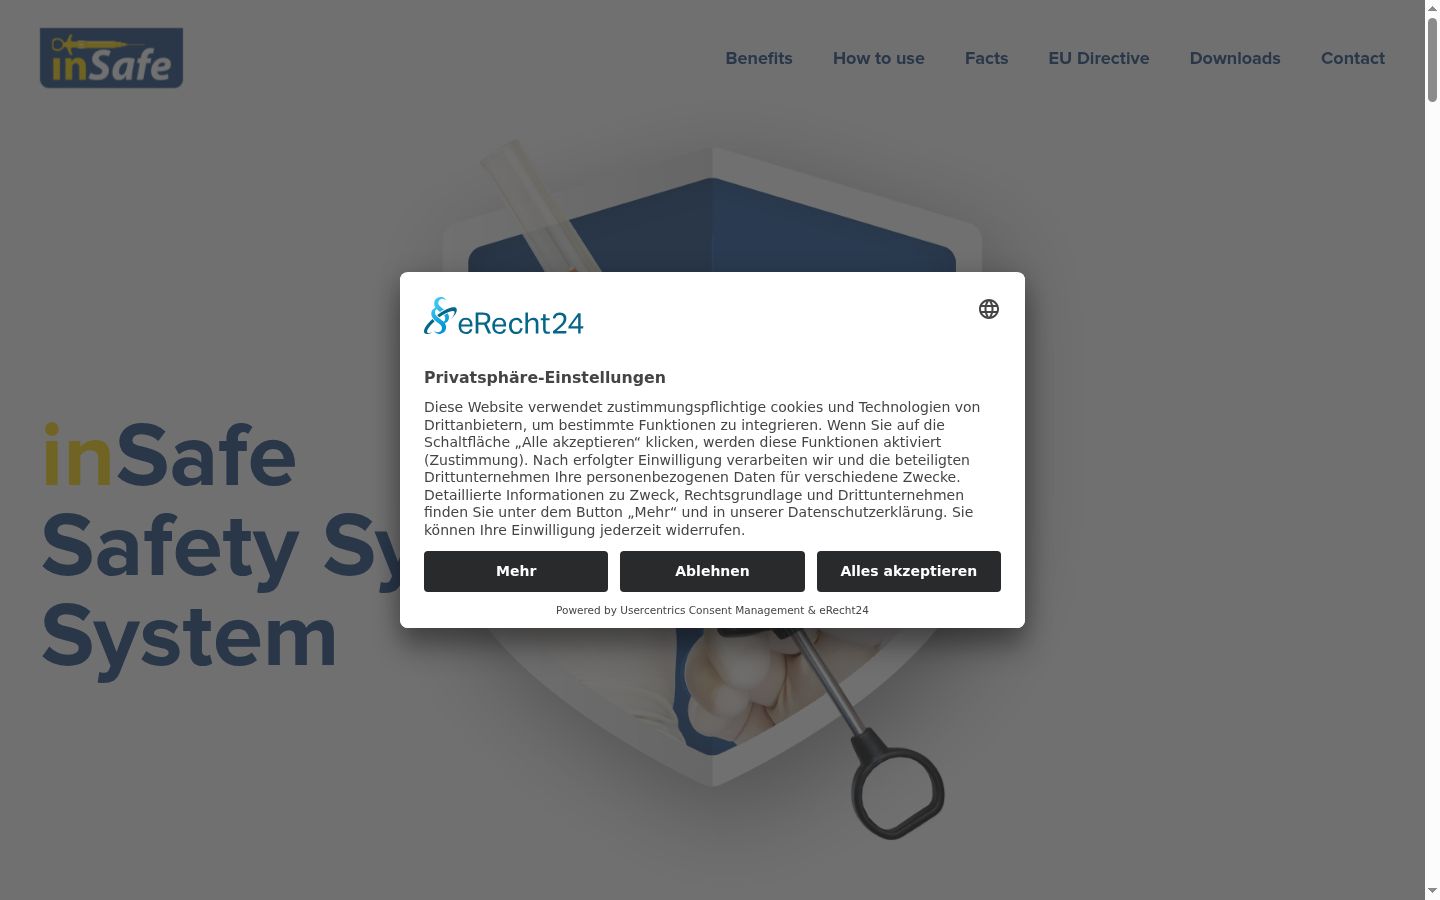
The first layer offers a Reject option alongside Accept.
Load timeline before consent
Milliseconds from navigation start until each request fired or each cookie was set.
Observed before consent
Cookies set before consent (2)
-
_gaanalytics · Google Analytics -
_ga_W3XF8PRK6Ganalytics · Google Analytics
Tracking requests before consent (4)
- Automattic stats.wp.com at 400 ms
- Google LLC www.googletagmanager.com at 399 ms
- Sentry (Functional Software) browser.sentry-cdn.com set by www.insafedental.eu/E-v1.js · at 660 ms
- Google LLC region1.google-analytics.com set by www.googletagmanager.com/js · at 524 ms
How we tested
Browser: Chrome/150.0.7871.124 · Scan origin: EU · Viewport: 1440×900 · Checked: 5 Oct 2026 04:31
Cookies
2
Third-party
0
Trackers
5
Vendors
4
Consent banner
Usercentrics
Scans
1
What this setup is missing
- Google tags were observed, but Google Consent Mode v2 was not detected.
Compliance by audience
European Union
✗ Not metGDPR + ePrivacy · Prior consent (opt-in)
United Kingdom
✗ Not metUK GDPR + PECR · Consent-based
United States
✓ Meets this modelCCPA/CPRA + state laws · Notice & opt-out
Canada
! Needs attentionPIPEDA + Québec Law 25 · Consent-based
Brazil
! Needs attentionLGPD · Consent-based
Scanned from the EU; sites may serve different banners or tracking to other regions. Verdicts reflect observed behaviour measured against each audience's rules.
Connection security
HTTPS supported
✓Redirects HTTP to HTTPS
✓HSTS
✗Content Security Policy
✗
Third-Party Trackers
5 requests detected from 4 vendors: Automattic, Google LLC, Sentry (Functional Software), Wistia
Third-Party Trackers
5 requests detected from 4 vendors: Automattic, Google LLC, Sentry (Functional Software), Wistia
Analytics
3
Marketing
0
Necessary
1
Functional
0
Other
1
| Vendor | Category | Type | Domain |
|---|---|---|---|
| Automattic before consent Automattic tracker domain (source: Disconnect.me, category: Content) | Analytics | script | stats.wp.com |
| Google LLC before consent Google Tag Manager | Analytics | script | www.googletagmanager.com |
| Sentry (Functional Software) before consent Sentry browser SDK | Analytics | script | browser.sentry-cdn.com |
| Wistia Wistia tracker domain (source: Disconnect.me, category: Content) | Necessary | script | fast.wistia.com |
| Google LLC before consent Google tracker domain (source: Disconnect.me, category: FingerprintingGeneral) | Unknown | script | region1.google-analytics.com |
Scan history
One completed scan: cookies and trackers from the scan on October 5, 2026.
Recent scans
| October 5, 2026 | 2 5 |
More Cookie Compliance Reviews

Medical Education
insideals.eu

Kontakt INSIDE STORIES - Interior Design in Mü...
inside-stories.eu

One moment, please...
inside-cove.eu

Ώρα για Αναβάθμιση!
inserenity.eu

Maintenance Prédictive Et Contrôle énergéti...
insens.eu

Insel und Hafenführer Ägäis - Die Insel Skyros
inselfuehrer-aegaeis.eu

Page par défaut
inscog.eu

L’Équipe – INQHAS
inqhas.eu
Is insafedental.eu your website?
Claim it to monitor your cookies and trackers, set up a consent banner with automatic script blocking, and keep your cookie policy up to date.